Blog
featured articles
Code Volume Diverged From Headcount. Pricing Must Follow
For most of AppSec's history, developer headcount was the only reliable number available, so it became the number the market priced against. More developers meant more code. More code meant more risk. Seat-based pricing and seat-based TAM models followed, and both held up for over a decade.
They don't anymore. And the TAM is considerably larger than the seat-based spreadsheets suggest.
The market was built on a correlation, not a cause
The old math was clean. As of 2021 there were roughly 28 million developers worldwide, about 60% of them at companies with more than 50 employees. Blend a per-seat price across the usual module set, SAST, SCA, secrets scanning, IaC, ASPM, and you land somewhere around $500 per developer per year. Multiply it out and the AppSec TAM comes to roughly $8.4 billion, projected to climb to around $14 billion by 2030 on the back of 3 to 5% annual headcount growth.
Not bad.
The model made sense because the correlation held. One developer produced roughly one developer's worth of code, so headcount was a fair stand-in for output. The seat was a unit that meant something. Every AppSec pricing page, and most of the TAM decks behind them, still run on that assumption, projecting the market forward by projecting hiring forward.
Five years later, professional developer headcount still grows in the low single digits. Code output left that curve. GitHub processed 986 million commits in 2025, a 25% jump in a single year after a decade of low-teens growth. Platform totals blend many things together, including a record year of new signups, so treat that number as directional.
The per-developer data is where the break shows up. Cursor's usage data shows mean lines added per developer per week climbing from 3.6K to 8.6K in about seventeen months. Lines added per pull request at the 75th percentile are up roughly 2.5x year over year. The growth rate is still accelerating.
Per seat pricing models stopped meaning anything.
Beyond volume, the seat itself stopped functioning as a stable unit. A marketing manager with the right tooling can ship more code in an afternoon than some backend engineers ship in a week. A team of ten, properly equipped, outproduces a team of hundreds running outdated practices. None of it shows up in a headcount projection, because headcount was never measuring output. It was measuring who had a badge and a laptop.
When a badge reliably produced a predictable amount of code, per-seat licensing made sense. Now a single seat can produce zero lines in a week or a thousand in an hour, generated by a swarm of agents running continuously against a codebase. A unit that can represent either reality at any given moment isn't a unit worth pricing against.
Once headcount stops tracking output, pricing products or sizing the market on it stops making sense. Code defines the attack surface, not the developer who happened to be logged in when it was written. Pricing and sizing product security against code produced is a straightforward correction.
The formula changed in five years:
2021: [seats] x [security modules]
2026: [code volume] x [risk]
Run the napkin math and the $14 billion 2030 projection looks conservative. A market growing in the low single digits and a market compounding past 25% a year part company fast. Within a few years they are no longer versions of the same forecast. They are different markets.
Not all code deserves the same scrutiny
The argument comes with an obvious caveat. Raw line counts aren't the whole answer, because all lines aren't created equal. A payment service and an internal dashboard do not deserve the same scan frequency, the same review depth, or the same scrutiny, even if they produce a comparable number of commits in a given week.
The real unit is risk-weighted code: what a change touches, who and what can reach it, how exploitable it is once it ships. Weight the volume by risk and the growth story holds. Risk-weighted volume grows slower than raw lines, since agents generate plenty of scaffolding and tests, but it still compounds an order of magnitude faster than headcount. The caveat narrows the number. It doesn't rescue the seat.
Risk weighting is also why validation matters more than finding count. A scanner that produces more alerts as code volume grows is describing the problem faster, at higher cost. Sizing and pricing against code volume holds up only if the code being counted is weighted by what it can do to the business.
Are we moving to consumption based AppSec?
I can't speak for the market. I can speak for Prime: we priced the product on consumption, because seats no longer count anything. Security context has to follow code and risk, from architecture through code to the running environment. A model priced on seats can't scale with a codebase that no longer scales with people.
If you're a buyer, run the test yourself. Chart your code volume against your headcount for the last eighteen months, then put that chart next to your security invoices. If the invoices track the flat line, you know which market your vendor is pricing. And stop negotiating what counts as an active developer. That fight exists because the unit is fake.
Consumption will cost some buyers more, and that's worth saying out loud. But the spend isn't new. The attack surface grew the moment the code shipped; a seat-based invoice just didn't register it. Risk-weighting keeps the meter honest: scaffolding shouldn't cost what a payment service costs. You pay for the risk you're carrying, which is the only number worth paying against.
Ready to see what it looks like to size and secure your codebase by what it actually produces, not by how many seats are logged in? Learn more at primesec.ai.
Cutting Through ProdSec Noise
Prioritizing Vulnerabilities by Context Driven Attack Paths, Not Severity Score
Open any vulnerability dashboard right now and you'll see the same thing every security team sees: more findings than anyone could review in a lifetime, ranked by severity scores that all cluster near the top. Roughly 48,000 new CVEs were published in 2025 alone, and the average program has bandwidth to remediate somewhere between 10 and 15 percent of its backlog in a given month. That gap between what gets found and what gets fixed isn't a staffing problem. It's noise, and it's been mistaken for a risk picture for long enough that most teams have stopped questioning it.
Vendors have started layering exploitability and reachability signals on top of severity scores, flagging whether a CVE has a known exploit in the wild or whether the vulnerable function is actually called by application code. That's a real step past CVSS alone, and it does cut some findings out of the queue. But exploitability and reachability answer "can this be exploited," not "does it matter here." A reachable, exploitable vulnerability in an internal tool with no sensitive data behind it is a different risk than the identical vulnerability in a service with a direct path to payment data, and exploitability scoring alone can't tell those two apart. Without the business and architectural context to make that distinction, exploitability and reachability data just re-sorts the same pile into a slightly different order. It doesn't reduce it.
Where All This Noise Comes From
Noise doesn't come from one bad scanner. It comes from the fact that every scanner you add reports its own findings in isolation, with no view of whether anything it flags actually connects to anything else. SAST grades code. SCA grades dependencies. Secret scanning grades commits. Each one is doing its job correctly, and each one is contributing its own independent stream of severity-ranked findings to a backlog that was already too large before it showed up.
That fragmentation was survivable when code shipped at human pace. AI coding agents have removed that constraint, and the backlog is growing with it. A developer opens a handful of pull requests a day; an agent working in the background can open dozens, and every one of them triggers its own pass from every scanner in the pipeline. The noise problem stopped being something a team could plan around once a quarter and became something that compounds with every commit an agent makes, which means the case for reducing it is no longer theoretical. It's urgent, and it gets more urgent by the day.
Adding tools to cover more of the stack feels like progress, and in a narrow sense it is. But it also means the noise compounds. Four scanners each reporting cleanly on their own slice of the product doesn't add up to a quieter picture of risk. It adds up to four separate streams of findings, none of which know about the other three, and that isolation is exactly what produces false positives and false confidence in the same breath. A scanner with no view of the environment has no way to know a downstream control already neutralizes what it just flagged, so it reports a real finding as urgent when it isn't. The opposite failure is just as common: without understanding how the surrounding system actually behaves, a tool can't verify whether a vulnerability it found is reachable in an actual attack path, which means genuine risk gets buried in the same pile as the noise around it.
Why More Noise Doesn't Mean More Security
The instinct is to sort the noise by severity and work top-down. That fails because severity measures how bad a vulnerability could theoretically be, not whether it's reachable, exposed, or exploitable in this specific environment. Two findings with identical CVSS scores can carry completely different risk depending on what's around them: one sits behind three layers of controls, the other has a direct path to production. A backlog sorted by severity alone treats those as the same problem, which is exactly why teams burn remediation capacity on findings that were never going anywhere while genuinely dangerous ones sit untouched further down the list.
Cutting Through the Noise Starts with One Question
Cutting through that noise isn't a matter of triaging faster or tuning the scoring model harder. It requires asking a different question of every finding, one severity scores were never built to answer: is this part of a path an attacker could actually walk right now, given what it connects to. And more importantly, how feasible is this path? If an exploit requires Tom Cruise to dangle dramatically from the ceiling, it’s unlikely to be prioritized by attackers. In other words, there is no simple solution that relies on a single score…which is exactly why context matters!
That's an execution-path question, not a severity question, and it changes what "important" means. A CVSS 9.8 sitting on a service with no route to anything sensitive isn't urgent, whatever the score says. A medium-severity finding sitting on a component that connects straight to a trust boundary might be the most important thing in the backlog. Severity describes a finding in isolation. An execution path describes what happens once you stop looking at scores and start focusing on the real impact to the business and how exposed the vertical to that impact.
What's Left When You Filter for Execution Paths
Run that filter honestly and the backlog doesn't just get shorter, it changes shape entirely. What's left isn't a smaller version of the same list sorted the same way. It's a small, specific set of findings that are reachable and chained together into something an attacker could actually use, the kind of path where a component that passes its own scan cleanly still turns out to be one link in a route to something that matters.
Building a Practice Around Signal, Not Volume
None of this is an argument for buying another scanner. Another scanner adds another stream of severity-ranked findings, which is exactly the problem, not the fix. What's needed is something that doesn't produce its own isolated list at all: a way of seeing the product as one connected system, where a finding is judged by what it opens up rather than scored and filed on its own.
SAST, SCA, and secret scanning were built to grade their own slice of the product well, not to reason across slices, and no amount of tuning changes that. What's missing is a layer above all of them, one that holds architecture, data flows, and access paths in view together and asks the question none of the individual scanners can: does this finding sit on a path an attacker could really walk, given everything else true about this product right now.
The Elephant in the Room: Developer Alert Fatigue
The noise problem doesn't stay in security's backlog. Every finding that reaches a developer without context asks them to stop and chase down whether it's real, and often it isn't: a downstream control already handles it, the path doesn't exist, the function isn't even called. After enough of those empty chases, the rational response isn't more diligence. It's discounting the next finding, and the one after that.
That erosion is the real cost. It isn't just inefficient for security teams triaging a backlog. It teaches developers, correctly, that most of what lands in their queue isn't worth their time, which means the findings that actually matter now have to fight through that learned skepticism to get acted on at all. The fix isn't more findings or sterner tickets. It's surfacing only what's already been checked against the path it would need to travel.
What This Means for Security Leaders
The measure of a good vulnerability management practice was never how many findings you closed this quarter. It's whether what's left in front of your team, after the noise is filtered out, is actually worth their time. A shorter list sorted by the same broken signal isn't progress. A list built from real execution paths, however short, is.
At Prime, this is the case for correlating findings against real execution paths across the whole product rather than triaging them one severity score at a time, so what reaches your team is what an attacker could actually walk, not everything a scanner happened to flag.
Ready to see what's left once the noise is filtered out? Learn more at primesec.ai.
Software Security Needs a New Unit to Review
For the last decade, the pull request has been the moment a developer's work paused long enough for someone else to look at it. That pause is what turned the PR into a checkpoint. A reviewer read the diff and checked it for whatever could go wrong: bugs, broken business logic, security holes. Nobody designed the PR to be a security control. It became one because it was the last place in the software lifecycle where a person reliably paid attention before code shipped.
Now agentic development is breaking the math that made the diff work. PRs are getting bigger and more frequent at the same time, and the pause they run through hasn't gotten any longer. The unit of review is shifting under security's feet.
Before anyone scanned PRs, security tools ran against whole repositories, and compliance programs accepted that as review. The results were unusable: thousands of noisy findings and no way to tell which ones mattered. So the industry moved down to the diff. It was the easiest unit to work with, not the right one.
The PR is changing. Drastically.
Look at what a pull request is actually made of: a diff, a comment thread, and an approval button. None of it was ever the control. It was just tooling built for the moment someone paused to review the work. The pause survived on three conditions. PRs stayed small enough to read closely. Rare enough that every one of them got read. And the review produced a handful of issues that a developer will actually fix.
Agentic development is killing all three at once. Cursor's enterprise data shows average PR size more than doubling, with volume up another 25% on top. Mega PRs, 1,000 lines or more, are now routine. A Microsoft study of Claude Code and GitHub Copilot CLI users found adopters merging roughly 24% more PRs, hitting 50% in heavy-use weeks and holding there for four months. And bigger PRs carry more issues per review, pushing every comment thread past the point where developers stop reading it.
Any one of these would strain a review built around a careful pause. Together they take away everything it needed: time per PR, few enough PRs to give each one that time, and findings scarce enough to get fixed.
What's actually inside all those new PRs
Volume is only half the problem. The other half is what's landing inside each PR. CodeRabbit's analysis of AI-co-authored pull requests found they carry roughly 1.7 times more issues than human-only PRs, including 1.5 to 2 times more security-relevant findings like improper credential handling and insecure object references. High-issue outliers cluster in AI-assisted work. So a reviewer doesn't know which PR needed the slow read until they've already skimmed past it.
Compliance programs accept PR approvals as evidence that changes were reviewed before deployment. Today, the audit trail looks exactly like it did three years ago. What's changed is what that approval means. It used to mean someone read the code. Now, on a 1,500-line agent-written PR that arrived with six others that morning, it mostly means the person ran out of reasons to keep it open. The requirement is still being met on paper. Whether real security is happening underneath is a separate question, and no audit is built to ask it.
The unit was always a proxy
Once you see the PR as a stand-in for attention rather than a control in its own right, the question changes. Scaling review to handle more, bigger PRs is the wrong project. The real question is where that attention needs to live now that it can't all sit in one checkpoint.
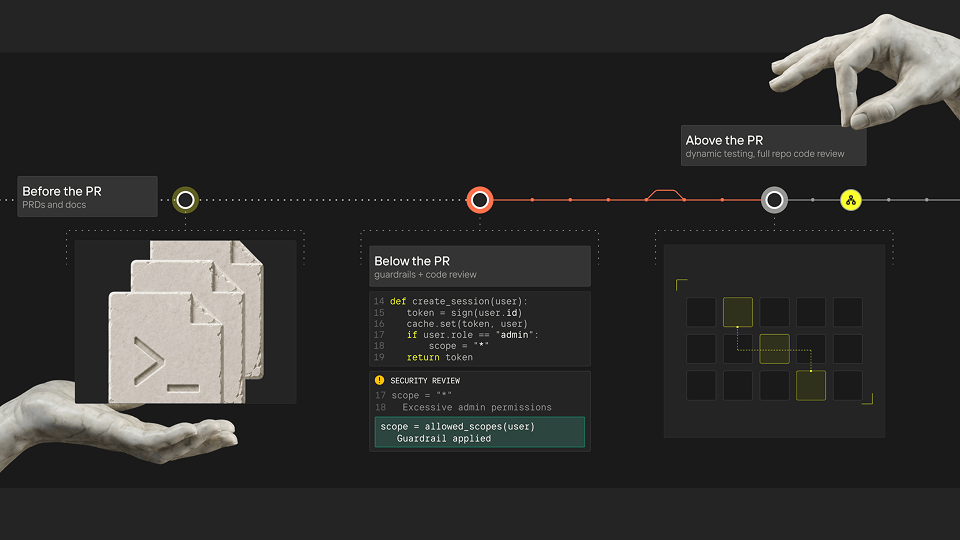
Some of it belongs below the PR, where an agent makes decisions in real time and context can be applied before a diff exists. Some belongs above it, at the repository level, because a vulnerability spread across several small, reasonable PRs never shows up in any single diff. And some belongs before the PR entirely, in the architecture and design decisions that shape what an agent, or a developer, can build in the first place.
The repository level is the one that should give people pause, because the industry has been there before. Repo-wide analysis is where this story started, and it collapsed under its own findings. But that was a context problem, not a level problem. The tools flagged patterns without knowing what was reachable, what was exploitable, or what mattered to the product. Analysis that traces attack vectors and validates exploitability before it surfaces anything produces the one thing the old scanners never could: a short list. Five findings a developer will actually fix, with a risk score that is attached to a product. The comment-count condition, restored at the level the industry abandoned.
So PR reviews are dead? Right? Right?
No, PR reviews aren't dead. The pause they measured is.
Reviews stay in the program as one place security happens, not the primary one. Attention has to live where decisions live now: in the design before code exists, in the code as it's written, in the repository as it evolves. This is what we do at Prime, that's the architecture: review the design, guard the code, trace attack vectors across the repo, dependencies, and cloud continuously.
PDLC and SDLC: Partners, Not Rivals – Security Practices
In part one of this two-part series, we established that PDLC (Product Development Life Cycle) encompasses SDLC (Software Development Life Cycle), and that organizations should adopt both rather than treating them as separate or interchangeable approaches, especially in a world where most “products” are software-based.
This second article dives into the security angle for both PDLC and SDLC. When discussing software security, the focus typically lands on SDLC alone. However, this approach is too narrow for a product-driven landscape. Why? Because SDLC covers only the software portion, while threats today spread far beyond the application code.
Comparing Security Practices of PDLC and SDLC
Here’s the reality: in a world where software companies do everything they can to deliver their products as fast as possible, security can’t just be about the code or the infrastructure. It must be about the product, end to end. That’s where the shift from SDLC-focused security to PDLC-focused security becomes critical. The PDLC isn’t just about building software, it’s about building and managing the entire product, from ideation to decommissioning. And in a modern threat landscape where risks extend far beyond the boundaries of application code, PDLC-focused security is how you keep your product and your business safe.
Let’s take a closer look again at the various stages of PDLC and SDLC but this time, let’s add another layer, security practices for per each framework:
| PDLC Stage | SDLC Stage | PDLC Security Practices | SDLC Security Practices |
|---|---|---|---|
| Idea Generation & Conceptualization | No direct SDLC equivalent | Identify preliminary regulatory/compliance needs, baseline security posture | N/A (No code yet, no direct SDLC security actions) |
| Market Research & Analysis | No direct SDLC equivalent | Evaluate compliance frameworks (HIPAA, PCI-DSS), data privacy laws, threat landscape | N/A (Still no code; SDLC security actions have not started) |
| Product Design & Definition | Requirements Analysis (SDLC) | Define overall product-level security requirements, ensure alignment with market-driven compliance | Translate product security requirements into software-level security threats and security specs (e.g., OWASP ASVS) |
| Prototyping & Feasibility Testing | System Design (SDLC) | Validate product-level security assumptions, ensure secure design patterns at product architecture level | Perform secure architecture reviews, map security controls into system design, identify critical code-level mitigations |
| Development & Engineering (Incl. Software) | Implementation (Coding) (SDLC) | Ensure supply chain security (third-party components), maintain compliance oversight, product-level data protection policies | Implement secure coding practices, conduct code reviews with a security focus, perform SAST/DAST |
| Testing & Quality Assurance (Full Product) | Testing (SDLC) | Execute full product-level penetration tests, validate supply chain integrity, ensure compliance audits | Conduct software-level vulnerability scanning, fuzz testing, IAST, and security regression tests |
| Go-To-Market (Marketing & Launch) | Deployment (SDLC) | Harden deployment environments at the product level (secure configurations, protected delivery channels), ensure compliance sign-off | Secure the software deployment pipeline, apply hardened configurations, finalize environment-level security settings |
| Post-Launch Support & Iteration | Maintenance (SDLC) | Continuous product-level security monitoring (SIEM, supply chain monitoring), periodic compliance reassessment, incident response planning | Apply patches, fix bugs, remediate software vulnerabilities, maintain secure coding and release practices |
| Product Retirement / Sunset | No direct SDLC equivalent | Secure decommissioning at product-level (data sanitization, IP protection), compliance check for final asset handling | Remove or archive code securely, ensure no residual software vulnerabilities remain accessible, revoke credentials |
Three crucial insights:
- In an Secure Product Life Cycle focused approach, security is introduced at a point where significant design and architectural decisions are already made
- Many existing security processes before stage four (Development & Engineering) are either nonexistent or conducted manually
- Across stages, there is one common thread - Context. Security Teams need business context in every step, from mapping the regulatory and compliance requirements to understanding when and why a product should be deprecated
The conclusion - Security should be integrated in every stage
Since organizations developing software-based products operate largely within the PDLC, security must be integrated into every stage, not just during code creation. Success in this model hinges on understanding the broader business context, which acts as the connective tissue across all phases. Tools like Prime Security can help automate and streamline this process, ensuring that security follows the product from concept to retirement.
HIPAA's New Rules: Security-by-Design Increases in Importance
HIPAA is raising the bar with new cybersecurity rules to protect electronic health information (ePHI). These updates aim to tackle breaches and compliance gaps head-on. For healthcare organizations building software systems, it’s a wake-up call: security needs to start at the design phase.
What’s New?
The proposed HIPAA updates bring significant changes, including:
"Addressable" vs "Required" distinction - The new rules make all security standards mandatory, ensuring that essential protections are implemented consistently across regulated entities
Comprehensive Risk Assessments - Software organizations must inventory their technology assets and map how ePHI flows through systems, offering full visibility into vulnerabilities. These assessments should be conducted regularly, with frequency based on the organization's risk environment, operational changes, and evolving threats. This ensures continuous alignment with compliance and risk management
Mandatory Encryption - Encryption for ePHI is now a baseline requirement, ensuring sensitive health information remains protected in transit and at rest. Software-enabled solutions must include encryption protocols by default to safeguard data, even during potential breaches or unauthorized access attempts
Robust Audit Trails - HIPAA now prioritizes detailed monitoring and logging of ePHI access. Software systems need transparent tracking to identify who accessed data, when, and why. This simplifies regulatory reporting and strengthens accountability
Scalability and Flexibility - The rules remain technology-neutral, enabling software organizations of any size to implement solutions that balance security and operational efficiency. Whether a startup or enterprise, scalable options are critical to staying compliant
The message is clear: retrofitting security won’t suffice. To remain HIPAA-compliant, software systems must integrate security at every stage, starting from design.
Why Security-by-Design Matters
For software organizations building HIPAA-compliant systems, integrating security at the design phase is essential. Here’s why:
Early Risk Mitigation - Design-stage security uncovers risks before they escalate into costly vulnerabilities. This aligns with HIPAA’s proactive focus on risk management and ensures workflows remain seamless
Streamlined Compliance - Embedding security early ensures systems meet HIPAA’s requirements, such as audit trails, encryption, and risk assessments. This reduces the complexity of audits and guarantees long-term compliance
Accelerated Development - Addressing security from the start avoids delays and costly rework, enabling faster releases without compromising quality. HIPAA highlights proactive measures to prevent deployment vulnerabilities
Resilience Against Threats - Healthcare software is a prime cyberattack target. Design-stage security mitigates risks like unauthorized access and breaches, aligning with HIPAA’s call for adaptable systems to combat evolving threats
How Prime Security Fits the Bill
Prime Security helps software-enabled organizations integrate regulatory frameworks like HIPAA directly into their PDLC:
- Continuous Risk Monitoring: Scans planned development work to flag potential HIPAA-related risks, such as gaps in data encryption or insufficient audit trails
- Proactive Mitigation: Provides actionable mitigation plans tailored to address identified risks before development progresses
- Seamless Integration: Embeds compliance and security recommendations directly into developer workflows for easy adoption
- Regulatory Alignment: Simplifies adherence to HIPAA’s requirements for encryption, risk assessments, and ePHI access logging
With Prime, integrating HIPAA compliance into the SDLC becomes seamless, reducing risks and building trust.
The Bigger Picture
HIPAA’s updates are a turning point for healthcare cybersecurity. Organizations adopting security-by-design will:
- Protect patient data efficiently
- Build trust with users and regulators
- Innovate without compromising safety
The future of HIPAA compliance isn’t reactive, it’s preventative. Prime Security is here to help software organizations lead the way.
PDLC and SDLC: Partners, Not Rivals – The Essential Guide
This blog post is part one of a two-part series exploring the synergy between product and software development frameworks and the critical role security plays within them. In this first article, we’ll focus on the essentials: how the Product Development Life Cycle (PDLC) provides the overarching structure, while the Software Development Life Cycle (SDLC) operates as a vital component within it. In part two, we’ll shift our focus to security, examining how it threads through both frameworks and the need to shift to a more comprehensive approach. Ready to dive in? Let’s begin.
Your Software is a part of your Products
Building software today is no small feat. It requires a balancing act of speed, complexity, and quality. In today’s world, when we hear the word “product,” one of the first things that comes to mind (if not the one and only) is software. Whether it’s a sleek app, a powerful platform, or a seamless service, software has become the heart of modern products. But this shift has created a unique challenge: there are frameworks designed for building products and frameworks specifically for writing software. And because software often is the product, it’s easy to see why these two distinct types of frameworks frequently get blurred together.
PDLC (Product Development Life Cycle) and SDLC (Software Development Life Cycle) are two of the most fundamental frameworks in the tech world, yet they’re often treated as synonyms. On the surface, it’s understandable since both are about planning, creating, and delivering something of value. However, PDLC and SDLC serve very different purposes. PDLC is about the what and why of the product; defining goals, understanding user needs, and planning how to meet them. SDLC, on the other hand, zeroes in on the how; the technical process of designing, coding, testing, and deploying the software to deliver the what.
When these frameworks get confused, it can lead to misaligned priorities, poor communication, wasted effort and siloed security approach. Teams might overlook the big-picture strategy while getting lost in technical execution, or vice versa. And in a world where software is the backbone of most products, understanding the difference between these two frameworks isn’t just helpful but rather critical for building successful, scalable, and secure solutions. Let’s unpack how PDLC and SDLC work together.
Comparing the PDLC and the SDLC
- PDLC (Product Development Life Cycle) is the end-to-end process that guides a product from an initial idea through research, design, development, launch, and ongoing refinement until eventual retirement. It looks beyond just the code, focusing on business goals, market needs, and the full customer experience
- SDLC (Software Development Life Cycle) is the structured approach within the PDLC that specifically addresses the creation and maintenance of the software components. It provides a methodical framework for planning, building, testing, deploying, and maintaining the software so that it meets its requirements effectively
Put simply, PDLC orchestrates the entire product journey, while SDLC concentrates on how the software inside that product is built and kept running.
| PDLC Stage | SDLC Stage | Overlap & Hierarchy |
|---|---|---|
| Idea Generation & Conceptualization | No direct SDLC equivalent | PDLC > SDLC. No software code yet; conceptualizing product vision and business case |
| Market Research & Analysis | No direct SDLC equivalent | PDLC > SDLC. Market needs and compliance considerations shape future technical decisions |
| Product Design & Definition | Requirements Analysis (SDLC) | Overlap begins: PDLC guides what the product must do; SDLC translates this into software requirements |
| Prototyping & Feasibility Testing | System Design (SDLC) | PDLC > SDLC. Product prototypes guide technical feasibility, including secure architectures |
| Development & Engineering (Incl. Software) | Implementation (Coding) (SDLC) | Strong overlap: The PDLC’s product build includes creating the software |
| Testing & Quality Assurance (Full Product) | Testing (SDLC) | Direct overlap: PDLC testing considers full product security; SDLC testing focuses on software vulnerabilities |
| Go-To-Market (Marketing & Launch) | Deployment (SDLC) | Partial overlap: PDLC includes full product rollout (marketing, distribution), SDLC deployment focuses on releasing code |
| Post-Launch Support & Iteration | Maintenance (SDLC) | Overlap: PDLC ongoing improvements may drive continuous software updates and patches in SDLC |
| Product Retirement / Sunset | No direct SDLC equivalent | PDLC > SDLC. Product lifecycle ends; software may be decommissioned |
Think of PDLC as the overarching blueprint you’d use to craft a bestselling book. It starts with understanding your audience, picking the right genre, outlining the story’s arc, and planning how you’ll publish, distribute, and market the final work. SDLC, on the other hand, is like the detailed process of writing the chapters, editing each sentence, fixing plot holes, and ensuring the language flows smoothly. In other words, while the PDLC is about shaping a novel that resonates with readers and finds success in the market, the SDLC is about making sure the prose itself is strong and coherent. Without a solid PDLC to guide the SDLC, you might write a beautifully polished manuscript that no one wants to read or overlook security risks that arise from decisions made outside the text itself.
Compliments not Competitors
While it’s tempting to think of product and software as interchangeable in today’s world where most products are software-based, they are not the same. Each requires its own methodology, and understanding the distinctions between PDLC and SDLC is key to ensuring success. That said, it’s not about choosing one over the other; it’s about recognizing how they complement each other. Ignoring either framework means risking critical oversights and especially when it comes to security which can lead to far-reaching consequences.
Why We Should Talk More About Product Security
We all know the following fact: software development is in overdrive. Agile, DevOps, cloud-native platforms, microservices, code co-pilots, you name it, have made shipping products faster and easier than ever. But here’s the catch: all that speed and innovation has created a tangled mess of interconnected parts. And when it comes to security, most teams are still trying to tackle the problem one layer at a time:infrastructure here, application code there, data somewhere else.
And while this still covers main areas of concern, it also slows the business down. Modern software products are more like intricate ecosystems than neat stacks. If you’re only looking at security layer by layer, you’re missing the big picture, and leaving your product open to serious risk. Risk that is not confined to a single layer, but sprawls across all of them.
The Problem with a Lack of Business Context
Let’s take a page out of the great movie Big Short, and look at how restaurants operate. Say you just built a new top-of-the-line restaurant, hired the best chef, and ensured the dining area is off the charts! But if you don’t understand how your customers move through the restaurant, their favorite dishes, or what drives repeat visits, you will be working hard to make the business work but could be focusing on the wrong things. Put simply, you will be losing money.
The same is true for product security. Without understanding the broader business context, security teams can’t make truly risk-driven decisions. This often leaves them riding in the dark, with the occasional streetlamp to guide them. In cloud-native products, where everything moves fast and every decision matters, security must align with the product’s goals.
The Challenge with Manual Security Reviews
At this point we expect you to stop and say, “don’t we already have security reviews to handle this? Aren’t they supposed to catch every potential issue, ensuring that every change and development is seen through the proper lens of security?” Technically, you’d be right; that’s exactly what security reviews are meant to do. But we are realists and not hopeless optimists: the process is still manual. It relies heavily on human effort, tracking changes, analyzing risks, and trying to keep up with the relentless pace of development.
Now let me adjust the question a bit: how can we secure the business when development velocity has skyrocketed, business logic evolves constantly, and security is overwhelmed with vertical security and is constantly understaffed? The gap is growing wider by the day.Without automation, context-driven insights, and a holistic approach, security teams are left playing catch-up, reacting to risks after they’ve already been introduced instead of preventatively mitigating them. If we’re going to keep up, the way we approach security reviews has to evolve.
Why Security Needs to Evolve
The reality is security can’t afford to be stuck in the past. Software development has evolved into a high-speed race where new features and updates are shipped daily. The business logic driving these changes is constantly shifting, and manual security processes just can’t keep up.
To meet these demands, security needs to shift its mindset. It’s no longer about simply protecting individual layers or running manual reviews when something big is about to be released.It’s about building a security framework that understands the business context, moves at the speed of development, and sees the product as a dynamic, interconnected ecosystem. This means integrating automation, embracing a secure by design mindset, and embedding security into every aspect of the product lifecycle. Only by evolving in this way can security teams keep up with the pace of innovation while not only protecting the business, but also enabling it from the ground up.
Can we expect developers to be security experts?
Secure development is challenging and can be a significant drain on time and resources. Adding security responsibilities to developers’ workloads can overwhelm teams and raise security risks for organizations.
The pressure is on
Development is moving faster than ever, with AI accelerating the pace to new heights. Developers want to focus on what they do best, building and shipping great products. But when security tasks are layered on top, it creates a difficult trade-off, often sacrificing security for speed.
We recently met an impressive Product Security team at a fast-growing fintech company. They had all the right processes and tools, yet a critical design vulnerability, a broken authentication, slipped into production. Why? Developers had pushed for a low-risk classification for the release. The fallout: an unplanned emergency patch and a month of lost development time.
This isn’t an isolated story. Many organizations report similar experiences: development teams often label risks as “medium” or “low,” only for critical vulnerabilities to sneak into production, triggering fire drills and costly late fixes.
The data speaks for Itself
Accelerated development cycles - traditional automation and modern AI tools are speeding up development cycles. Great for innovation and velocity, but it also means that design risk increases if security guidance isn’t seamlessly integrated into the process
Growing complexity - with expanding tech stacks, developers need just-in-time guidance on integrating new technologies into their products and features.Code scanning alone can’t provide this support
Rising late remediations – despite the focus on secure development, the bug bounty and pen testing markets are expanding faster than ever, reflecting that vulnerabilities still slip through, demanding costly late fixes.
High developer turnover – developers change roles frequently, often staying for less than two years. By the time they’re trained on secure practices, they may move on, leaving knowledge gaps and disrupting the organization’s security continuity
Finding the real solution
Rather than expecting developers to shoulder security independently, organizations need to embed security directly into the development process - automated, integrated, and always present. This approach ensures developers receive consistent, reliable guidance without interrupting their workflow or slowing innovation.
Seamless integration of security into existing workflows allows developers to stay focused on what they do best, develop. With the right guidance, at the right time, they can make informed security decisions effortlessly.
At Prime, we make security guidance as seamless as your code deployments.
Our integrated approach ensures your team has the support they need, when they need it, for secure, rapid development. Ready to streamline security without slowing your development team down? Reach out to see how we can help.
Security by Design: Regulatory Requirements in October 2024
Building Secure Foundations: The Shift Towards Security by Design
“Security by Design” is no longer a best practice - it is a regulatory auditable imperative. Various global standards and frameworks now mandate that organizations adopt SbD principles to ensure compliance with data protection, privacy, and cybersecurity regulations.
Traditionally, security is reactive—addressed only after systems were developed or, worse, once a breach had already occurred. The limitations of this reactive approach have driven the emergence of the “Security by Design” philosophy, which prioritizes the integration of security measures right from the earliest stages of design and development. This principle has become a foundational aspect of the Software Development Lifecycle (SDLC), embedding security directly into the architecture of systems and products from the ground up.
Rather than relying solely on reactive methods like scanning run-time systems or identifying vulnerabilities after deployment, “Security by Design” focuses on preventing these risks much earlier in the process. It ensures that security considerations are a core element of the product development journey, reducing the likelihood of security flaws and minimizing the need for costly, time-consuming fixes later.
Regulators and international standards bodies have recognized the value of this approach. By incorporating “Security by Design” into the various frameworks, they are urging organizations to proactively identify potential security gaps and vulnerabilities, embedding robust security safeguards from the inception of any product or system. This shift towards a preemptive security strategy represents a significant evolution in how security is conceptualized and implemented across industries.
Relevance by Regulatory Framework
The table below outlines the “Security by Design” requirements within the current regulatory landscape and explains how organizations can achieve both procedural and technological compliance requirements with Prime Security.
NIST
The National Institute of Standards and Technology (NIST) is a U.S. government agency that develops and promotes measurement standards, technology, and science to enhance economic security and quality of life.
| Standard Name | Control/Requirement ID | Control/Requirement Description | Compliance with Prime |
|---|---|---|---|
| NIST CSF 2.0 | Platform Security (PR.PS) | PR.PS-06 Secure software development practices are integrated, and their performance is monitored throughout the software development life cycle | Prime incorporates secure development practices during the design phase and automatically identifies security risks |
| CA-02(02) Control Assessments | Specialized Assessments | Specialized assessments can also be conducted early in the system development life cycle (e.g., during initial design, development, and unit testing). | Prime facilitates the early identification of security risks by conducting security assessments during the initial design stage of system development lifecycle | |
| SA-03 System Development Life Cycle | a. Acquire, develop, and manage the system using an organization-defined system development life cycle that incorporates information security and privacy considerations. | Prime incorporates security and privacy requirements into the organization's SDLC by identifying risks early in the design phase | |
| SA-03 System Development Life Cycle | d. Integrate the organizational information security and privacy risk management process into system development life cycle activities. | Prime embeds the organization's security and privacy engineering principles or industry best practices into the design phase of SDLC | |
| SA-08 Security and Privacy Engineering Principles | Apply the organization-defined systems security and privacy engineering principles in the specification, design, development, implementation, and modification of the system and system components. | ||
| NIST 800-53r5 | SA-08 Security and Privacy Engineering Principles | Ensure that the systems security and privacy engineering principles are applied throughout the system development life cycle. | Prime embeds security and privacy requirements at the design stage, ensuring they are upheld throughout the SDLC |
| NIST 800-53r5 | PM-07 Enterprise Architecture | Integrate security and privacy requirements and controls into the enterprise architecture to ensure they are addressed throughout the system development life cycle and are explicitly related to the organization's mission and business processes. | Prime embeds security and privacy requirements at the design stage, ensuring they are upheld throughout the SDLC |
| NIST 800-53r5 | RA-08 Privacy Impact Assessments | Conduct privacy impact assessments for systems, programs, or other activities before developing or procuring information technology that processes personally identifiable information. | Prime identifies engineering tasks that could potential cause privacy violations prior to them being started |
ISO
The International Organization for Standardization (ISO) is a global body that develops and publishes international standards for products, services, and systems across various industries.
| Standard Name | Control/Requirement ID | Control/Requirement Description | Compliance with Prime |
|---|---|---|---|
| ISO/IEC 27001:2022(E) | 8.26 Application security requirements | Control: Information security requirements shall be identified, specified and approved when developing or acquiring applications. | Prime integrates into the organizational system development life cycle, detects and mitigates security gaps in the requirements given to systems and projects |
| ISO/IEC 27001:2022(E) | 5.8 Information security in project management | Control: Information security shall be integrated into project management. | Prime integrates information security into project management by embedding security requirements and risk assessments as early as possible in the development lifecycle |
| ISO/IEC 27002:2022(E) | 5.8 Information security in project management |
Control: Information security should be integrated into project management. Purpose: To ensure information security risks related to projects and deliverables are effectively addressed in project management throughout the project life cycle. Guidance: Information security should be integrated into project management to ensure information security risks are addressed as part of the project management. This can be applied to any type of project regardless of its complexity, size, duration, discipline or application area (e.g. a project for a core business process, ICT, facility management or other supporting processes). The project management in use should require that:
Early consideration of information security requirements for the product or service (e.g. at the planning and design stages), can lead to more effective and cost-efficient solutions for quality and information security. |
Prime integrates information security into project management by ensuring that security risks are assessed and treated early and periodically throughout the project lifecycle. It incorporates security requirements, such as application security and intellectual property compliance, from the planning and design stages, leading to more effective and cost-efficient solutions |
| ISO/IEC 27002:2022(E) | 8.25 Secure development life cycle |
Control: Rules for the secure development of software and systems should be established and applied. Purpose: To ensure information security is designed and implemented within the secure development life cycle of software and systems. Guidance:
|
Prime helps establish and apply rules for the secure development of software and systems by embedding information security requirements into the specification and design phases of the development lifecycle. This ensures that security is integrated from the outset, providing a foundation for building robust and secure applications |
| ISO/IEC 27002:2022(E) | 8.27 Secure system architecture and engineering principles |
Control: Principles for engineering secure systems should be established, documented, maintained and applied to any information system development activities. Purpose: To ensure information systems are securely designed, implemented and operated within the development life cycle. Guidance: Security engineering principles should be established, documented and applied to information system engineering activities. Security should be designed into all architecture layers (business, data, applications and technology). New technology should be analyzed for security risks and the design should be reviewed against known attack patterns. Secure engineering principles provide guidance on user authentication techniques, secure session control and data validation and sanitisation. Secure system engineering should involve:
|
Prime helps organizations establish, document, and maintain secure system engineering principles throughout the development lifecycle, ensuring security is integrated into all architecture layers—business, data, applications, and technology. It supports security-by-design practices, such as "defense in depth," "least privilege," and "default deny," while guiding security-oriented design reviews to identify vulnerabilities and ensure adequate controls are in place |
PCI-DSS v4.0
The Payment Card Industry Data Security Standard (PCI DSS) is a set of security requirements designed to ensure that all companies that process, store, or transmit credit card information maintain a secure environment.
| Control/Requirement ID | Control/Requirement Description | Compliance with Prime |
|---|---|---|
| Requirement 6: Develop and Maintain Secure Systems and Software | 6.2.1: Incorporating consideration of information security issues during each stage of the software development lifecycle. | Prime incorporates information security considerations during the design stage of the software development lifecycle, ensuring that potential risks are identified and addressed early. This proactive approach reduces the likelihood of discovering security vulnerabilities at later stages, minimizing costly rework and enhancing overall system security |
HITRUST
The HiTRUST (Health Information Trust Alliance) CSF (Common Security Framework) is a comprehensive security framework designed specifically for the healthcare industry. It combines and harmonizes various standards and regulations, including HIPAA, PCI, and ISO, to provide organizations with a unified approach to managing information security and privacy risks in healthcare.
| Control/Requirement ID | Control/Requirement Description | Compliance with Prime |
|---|---|---|
| Control Category: 10.0 - Information Systems Acquisition, Development, and Maintenance |
Control Objective: To ensure that security is an integral part of information systems. Control Specification: Statements of business requirements for new information systems (developed or purchased), or enhancements to existing information systems shall specify the requirements for security controls. Specifications for the security control requirements include security controls to be incorporated in the information system, and supplemented by manual controls as needed. Further, security control requirements are considered when evaluating software packages, either developed or purchased. |
Prime ensures that security is an integral part of information systems by embedding security control requirements into the specifications for new or enhanced systems. This approach ensures that security requirements are considered from the outset |
CSA controls matrix v4.0.12
The Cloud Security Alliance (CSA) Cloud Controls Matrix (CCM) is a cybersecurity control framework specifically designed for cloud computing environments. It provides a comprehensive set of cloud-specific security controls to help organizations assess and improve their cloud security posture, align with various regulations, and enhance overall risk management in cloud deployments.
| Control/Requirement ID | Control/Requirement Description | Compliance with Prime |
|---|---|---|
| Application & Interface Security Secure Application Design and Development (AIS-04) | Define and implement a SDLC process for application design, development, deployment, and operation in accordance with security requirements defined by the organization. | Prime integrates the organization's security requirements into the SDLC by identifying risks and defining security controls during the application design phase |
| Data Security and Privacy Lifecycle Management Data Protection by Design and Default (DSP-07) |
Develop systems, products, and business practices based upon a principle of security by design and industry best practices. | Prime enables the development of systems, products, and business practices based on the principle of security by design and aligned with industry best practices. It incorporates security requirements from the outset, ensuring that security is embedded throughout the development process |
| Data Security and Privacy Lifecycle Management Data Privacy by Design and Default (DSP-08) |
Develop systems, products, and business practices based upon a principle of privacy by design and industry best practices. Ensure that systems' privacy settings are configured by default, according to all applicable laws and regulations. | Prime automatically identifies potential privacy violations during the design stage, ensuring that privacy requirements are integrated from the outset. It helps configure systems' privacy settings by default to comply with applicable laws and regulations, following the principle of privacy by design and industry best practices |
COBIT 5
Control Objectives for Information and Related Technologies (COBIT) is a framework created by ISACA for information technology (IT) management and IT governance. It provides a set of best practices for aligning IT with business objectives, optimizing IT resources, and managing IT-related risks and controls across an organization.
| Control/Requirement ID | Control/Requirement Description | Compliance with Prime |
|---|---|---|
| BAI01 - Manage Programmes and Projects BAI01.09 - Manage programme and project quality |
1. Identify assurance tasks and practices required to support the accreditation of new or modified systems during programme and project planning, and include them in the integrated plans. Ensure that the tasks provide assurance that internal controls and security solutions meet the defined requirements. | Prime identifies compliance and regulatory violations at the design stage, ensuring that any issues are addressed early to support the accreditation of new or modified systems. By integrating these assurance tasks into project planning, it provides confidence that internal controls and security solutions meet defined requirements from the outset. |
| BAI02 - Manage Requirements BAI02.04 - Obtain approval of requirements and solutions |
1. Ensure that the business sponsor or product owner makes the final decision with respect to the choice of solution, acquisition approach and high-level design, according to the business case. Coordinate feedback from affected stakeholders and obtain sign-off from appropriate business and technical authorities (e.g., business process owner, enterprise architect, operations manager, security) for the proposed approach. | Prime enables the business sponsor or product owner to make informed decisions on the solution, acquisition approach, and high-level design by identifying security risks early in the design stage. It provides insights into potential vulnerabilities and gathers feedback from stakeholders, ensuring that decisions are aligned with both business objectives and security requirements. |
| BAI03 - Manage Solutions Identification and Build BAI03.01 - Design high-level solutions |
3. Create a design that is compliant with the organization's design standards, at a level of detail that is appropriate for the solution and development method and consistent with business, enterprise and IT strategies, the enterprise architecture, security plan, and applicable laws, regulations and contracts. | Prime ensures that designs comply with organizational standards by identifying security requirements and risks early in the development process. It aligns the design with business, enterprise, and IT strategies, the enterprise architecture, security plans, and relevant laws, regulations, and contracts. |
| BAI03 - Manage Solutions Identification and Build BAI03.02 - Design detailed solution components |
9. Proactively evaluate for design weaknesses (e.g., inconsistencies, lack of clarity, potential flaws) throughout the life cycle, identifying improvements when required. | Prime focuses on identifying security flaws during the design phase by evaluating potential weaknesses, such as inconsistencies, ambiguities, and vulnerabilities. It provides early insights and recommendations for improvement, ensuring that security issues are addressed before they progress further in the development lifecycle. |
Institute of Internal Auditors
The Institute of Internal Auditors (IIA) is a global professional association that serves as the primary advocate, educator, and standard-setter for the internal audit profession. It provides guidance, certifications, and resources to enhance the effectiveness of internal auditors in various industries, promoting ethical practices and professional excellence in risk management, control, and governance processes.
| Control/Requirement ID | Control/Requirement Description | Compliance with Prime |
|---|---|---|
| F. How the organization addresses cybersecurity within their system development life cycle, including the following control aspects | 1. Planning: Cybersecurity has been identified as a key component when assessing risks and analyzing potential vulnerabilities. The scope and objectives of the software implementation should be included as the organization evaluates cybersecurity controls during the planning phase. |
Prime integrates cybersecurity risk assessments and compliance checks throughout the planning, requirements-gathering, and design phases of the SDLC. It identifies vulnerabilities early, ensures alignment with legal and regulatory standards, and recommends the necessary security controls that should be applied. Prime enables cyber security auditors to perform an effective audit process to ensure that security controls are being implemented at the design stage including formal audit evidence gathering. |
OWASP ASVS v4.0.3
Open Web Application Security Project (OWASP) is a nonprofit foundation dedicated to improving the security of software. It provides freely available articles, methodologies, documentation, tools, and technologies in the field of web application security.
| Control/Requirement ID | Control/Requirement Description | Compliance with Prime |
|---|---|---|
| V1.1 Secure Software Development Lifecycle | 1.1.1 Verify the use of a secure software development lifecycle that addresses security in all stages of development | Prime integrates into the design phase of SDLC and provides the proper security practices before actual development starts |
CIS
The Center for Internet Security (CIS) is a nonprofit organization that develops and promotes best practice standards for cyber defense. CIS provides benchmarks, controls, and tools to help organizations improve their cybersecurity posture, with a focus on creating and maintaining consensus-based, vendor-agnostic security configuration guidelines for various IT systems and software.
| Control/Requirement ID | Control/Requirement Description | Compliance with Prime |
|---|---|---|
| Control 16 - Application Software Security | 16.1 Establish and maintain a secure application development process. In the process, address such items as: secure application design standards, secure coding practices, developer training, vulnerability management, security of third-party code, and application security testing procedures. Review and update documentation annually, or when significant enterprise changes occur that could impact this Safeguard. | Prime enables organizations to establish and maintain a secure application development process by identifying risks early and recommending security requirements aligned with best practices |
GDPR
The General Data Protection Regulation (GDPR) is a comprehensive data privacy law enacted by the European Union in 2018. It sets strict rules for how organizations must handle personal data of EU residents, including requirements for consent, data protection measures, and individuals' rights over their data.
| Control/Requirement ID | Control/Requirement Description | Compliance with Prime |
|---|---|---|
| Article 25 - Data Protection by Design and by Default |
1. Taking into account the state of the art, the cost of implementation and the nature, scope, context and purposes of processing as well as the risks of varying likelihood and severity for rights and freedoms of natural persons posed by the processing, the controller shall, both at the time of the determination of the means for processing and at the time of the processing itself, implement appropriate technical and organizational measures, such as pseudonymisation, which are designed to implement data-protection principles, such as data minimisation, in an effective manner and to integrate the necessary safeguards into the processing in order to meet the requirements of this Regulation and protect the rights of data subjects. 2. The controller shall implement appropriate technical and organizational measures for ensuring that, by default, only personal data which are necessary for each specific purpose of the processing are processed. |
Prime helps organizations comply with data protection regulations by identifying cybersecurity risks during the design stage of the SDLC |
European Commission, Cyber Resilience Act
The European Commission is the executive branch of the European Union (EU). It proposes and enforces legislation, implements policies, and manages the day-to-day operations of the EU.
| Control/Requirement ID | Control/Requirement Description | Compliance with Prime |
|---|---|---|
| Proposal for a REGULATION OF THE EUROPEAN PARLIAMENT AND OF THE COUNCIL on horizontal cybersecurity requirements for products with digital elements and amending Regulation (EU) 2019/1020 | (1) create conditions for the development of secure products with digital elements by ensuring that hardware and software products are placed on the market with fewer vulnerabilities and that manufactures take security seriously throughout a product's life cycle. | Prime enables the development of secure products with digital elements by identifying vulnerabilities early in the design phase and ensuring they are minimized before market release. |
Monetary Authority of Singapore
The Monetary Authority of Singapore (MAS) is Singapore's central bank and integrated financial regulator. It oversees all financial institutions in Singapore, manages the country's exchange rate, operates its monetary policy, and works to ensure financial stability.
| Control/Requirement ID | Control/Requirement Description | Compliance with Prime |
|---|---|---|
| 5.4 System Development Life Cycle and Security-By-Design | 5.4.2 The security-by-design approach refers to building security in every phase of the SDLC in order to minimize system vulnerabilities and reduce the attack surface. The FI should incorporate security specifications in the system design, perform continuous security evaluation, and adhere to security practices throughout the SDLC. | Prime implements a security-by-design approach by embedding specific security requirements during the design phase of the SDLC to minimize vulnerabilities and reduce the attack surface. It continuously evaluates the system for security risks and ensures adherence to best practices throughout development. |
| 5.6 System Design and Implementation | 5.6.1 As part of the design phase, the FI should review the proposed architecture and design of the IT system, including the IT controls to be built into the system, to ensure they meet the defined requirements, before implementation. | Prime facilitates the review of the proposed IT system architecture and design during the design phase to ensure that all security controls align with defined requirements. |
The Future of Security by Design in Agile and CI/CD Environments
The evolution of Security by Design from a reactive, optional approach to a regulatory guideline reflects the increasing importance of cybersecurity in the modern world. As cyber threats continue to evolve, organizations can no longer afford to treat security as an afterthought. SbD ensures that security is a foundational element of system architecture, and compliance with international standards is critical to maintaining secure, resilient systems. By embracing SbD principles, organizations can protect their assets, meet regulatory requirements, and build trust with users in an increasingly interconnected digital landscape.
The rise of Agile development, alongside Continuous Integration and Continuous Delivery (CI/CD) practices, presents new challenges to the current, manual approaches. As CI/CD pipelines speed up the development and deployment cycles, the rapid pace of automation can reduce the capacity of human security architects to deliver timely and precise security guidance, and hence become a blocker to the business. To effectively address these challenges, the “Security by Design” framework must be reinforced by automated software tools, such as Prime, that can integrate security checks and controls seamlessly into the accelerated development process.
Product Velocity is Dependent on Product Security
The Cost of Security Stepping in Too Late
It’s a common problem: product development is moving fast, but once security steps in late, everything slows down. As companies grow and products become more complex, security often gets pushed to the end of the process. By then, code is written, deadlines are looming, and vulnerabilities surface. The result? Expensive delays and missed opportunities:
- Development teams scramble to rework code, adding up to 40% more time to the release cycle.
- Release schedules slip, increasing operational costs by 20-30%.
- Customers grow frustrated as features are delayed, leading to negative feedback.
- The relationship between Security and Engineering becomes strained, slowing progress even further.
This isn’t just frustrating—it’s costly. Fixing security issues late in the process can cost up to 10 times more than addressing them earlier. The core issue? Security and engineering aren’t working together early enough.
It's a People, Process, and Technology Problem
Today, companies rely on traditional security processes such as Security Design Reviews, Threat Modeling, and Security Champions programs to bridge the gap between Security and Engineering. According to the SANS DevSecOps Survey, most organizations recognize the value of up-front risk assessments, with over 80% of respondents acknowledging the benefits of early security involvement. However, few consistently implement these assessments early in the development process.
Why? It’s not just a technology issue—it’s a people and process problem too. Security design reviews and threat modeling are often manual, time-consuming, and difficult to scale across fast-moving development cycles. Programs like Security Champions, while valuable in theory, suffer from inconsistent adoption and execution, leaving critical gaps that can be costly to address later.
In a world where businesses need to move quickly to stay competitive, relying on manual, late-stage security processes becomes a significant bottleneck. Addressing vulnerabilities during the design phase is up to 10x cheaper and 70% faster than fixing them post-release. For organizations that rely on fast, iterative releases, every delay can compound, affecting market share, customer satisfaction, and overall growth.
Prime Security’s Approach
At Prime Security, we focus on maintaining product velocity by seamlessly integrating security into the planning and design phases, without disrupting existing workflows. Our platform connects directly with your company’s development tools—like Jira and Confluence—so security becomes part of the process without requiring developers to change their behavior. By automating the identification of risks and providing full visibility into potential issues before any code is written, Prime Security enables teams to take a preventative approach, addressing critical concerns early and keeping development on track. Rather than overwhelming developers with complex security tasks, we simplify the process by offering clear, actionable insights that allow Security and Engineering to collaborate efficiently. Prime Security delivers immediate time-to-value, with actionable insights available within 24 hours of implementation, ensuring teams can avoid last-minute delays and keep the development pipeline running smoothly.
Final Thoughts
When security is left to the end of the development process, product velocity inevitably suffers. But when Security and Engineering collaborate from the start, teams can avoid delays, meet their deadlines, and deliver secure, reliable products faster. By embedding security in the design phase, companies not only prevent costly delays but also gain a competitive advantage by consistently delivering secure, high-quality products at speed. At Prime Security, we help companies shift security left, empowering teams to move quickly without sacrificing security.